- Block length = 8 bytes
- Key length = from one byte up to 128 bytes
RC2 is a block symmetric cipher which was popular in the first half of the 90s of the last century. It was greatly promoted by the US government agencies.
Usage
RC2 was designed by Ron Rivest of RSA Security in 1987, who created also a few other ciphers. RC2 algorithm had been kept secret until 1996, when it was anonymously posted on sci.crypt group.
RC2 is also known as ARC2. The acronym RC is understood as "Rivest Cipher" or "Ron's Code".
Algorithm
RC2 is a block cipher, and the block size is 8 bytes (64 bits). This means that the input data is first divided into blocks of 8 bytes and then each of them is processed separately.
Each data block is treated as four words, each word has 16 bits (2 bytes). The array of four words is presented as R[0] R[1] R[2] R[3]. Both encryption and decryption take this array as input and modify the four words. The output is returned in the same array.
Key Expansion
Apart from the data, the RC2 cipher takes as input a secret user key. The key provided by the user may be of size from one byte up to 128 bytes. Let us denote the key size (in bytes) as Keysize. The first operation which RC2 then performs is to expand the key, to receive new 128 key bytes which will be used for encryption or decryption of all data bytes.
The user provides also a second value, denoted Keybit-limit, which determines the maximum effective key size, provided in bits. This means, that no matter how many bytes of the secret key has been provided by the user, the cipher will operate on the key which effective size is Keybyte-limit, where:
Keybyte-limit = (Keybit-limit + 7) / 8
Of course, the real strength of the key will be even smaller, if the user provided less key bytes than Keybyte-limit.
In order to assure that only that many bits will be used to secure the data, the following bit mask is defined:
Keymask = 255 mod 2^(8 + Keybit-limit - 8·Keybyte-limit)
The 8 - (8·Keybyte-limit - Keybit-limit) least significant bits of Keymask are set, the rest are zeros.
Key Words and Bytes
The mathematical operations that are performed on the key operate on both single bytes and whole words. So, for convenience, the numbers in the key may be presented as either 64 words:
K[0], K[1], ..., K[63]
or 128 separate bytes:
L[0], L[1], ..., L[127].
Note, that each part of the key array may be addressed by using either bytes or words. The following equation can be defined:
K[i] = L[2·i] + 256·L[2·i+1]
The low-order eight bits of each word is located before the high-order byte.
Key Expansion Algorithm
The first step of the key expansion algorithm is to fill the first Keysize bytes of key array with the bytes received from the user:
L[0], L[1], ..., L[Keysize-1].
Then, the following steps are performed on the key data. TPI mentioned below is a fixed array of size 256, filled randomly with values from 0 to 255:
- For i = Keysize, Keysize+1, and up until 127:
L[i] = TPI[(L[i-1] + L[i-Keysize]) mod 256] - L[128-Keybyte-limit] = TPI[L[128-Keybyte-limit] & Keymask]
- For i = 127-Keybyte-limit, down until 0:
L[i] = TPI[L[i+1] XOR L[i+Keybyte-limit]]
The effective encryption key is determined by the bytes:
L[128-Keybyte-limit], L[128-Keybyte-limit+1]..., L[127]
The operation & performed in the second step above limits the effective size of the key down to just Keybit-limit bits.
Encryption
The encryption procedure takes as input four words: R[0] R[1] R[2] R[3], which form one block of data. Every block of data will be encrypted by using the same 64 words of expanded secret key: K[0] K[1] ... K[63].
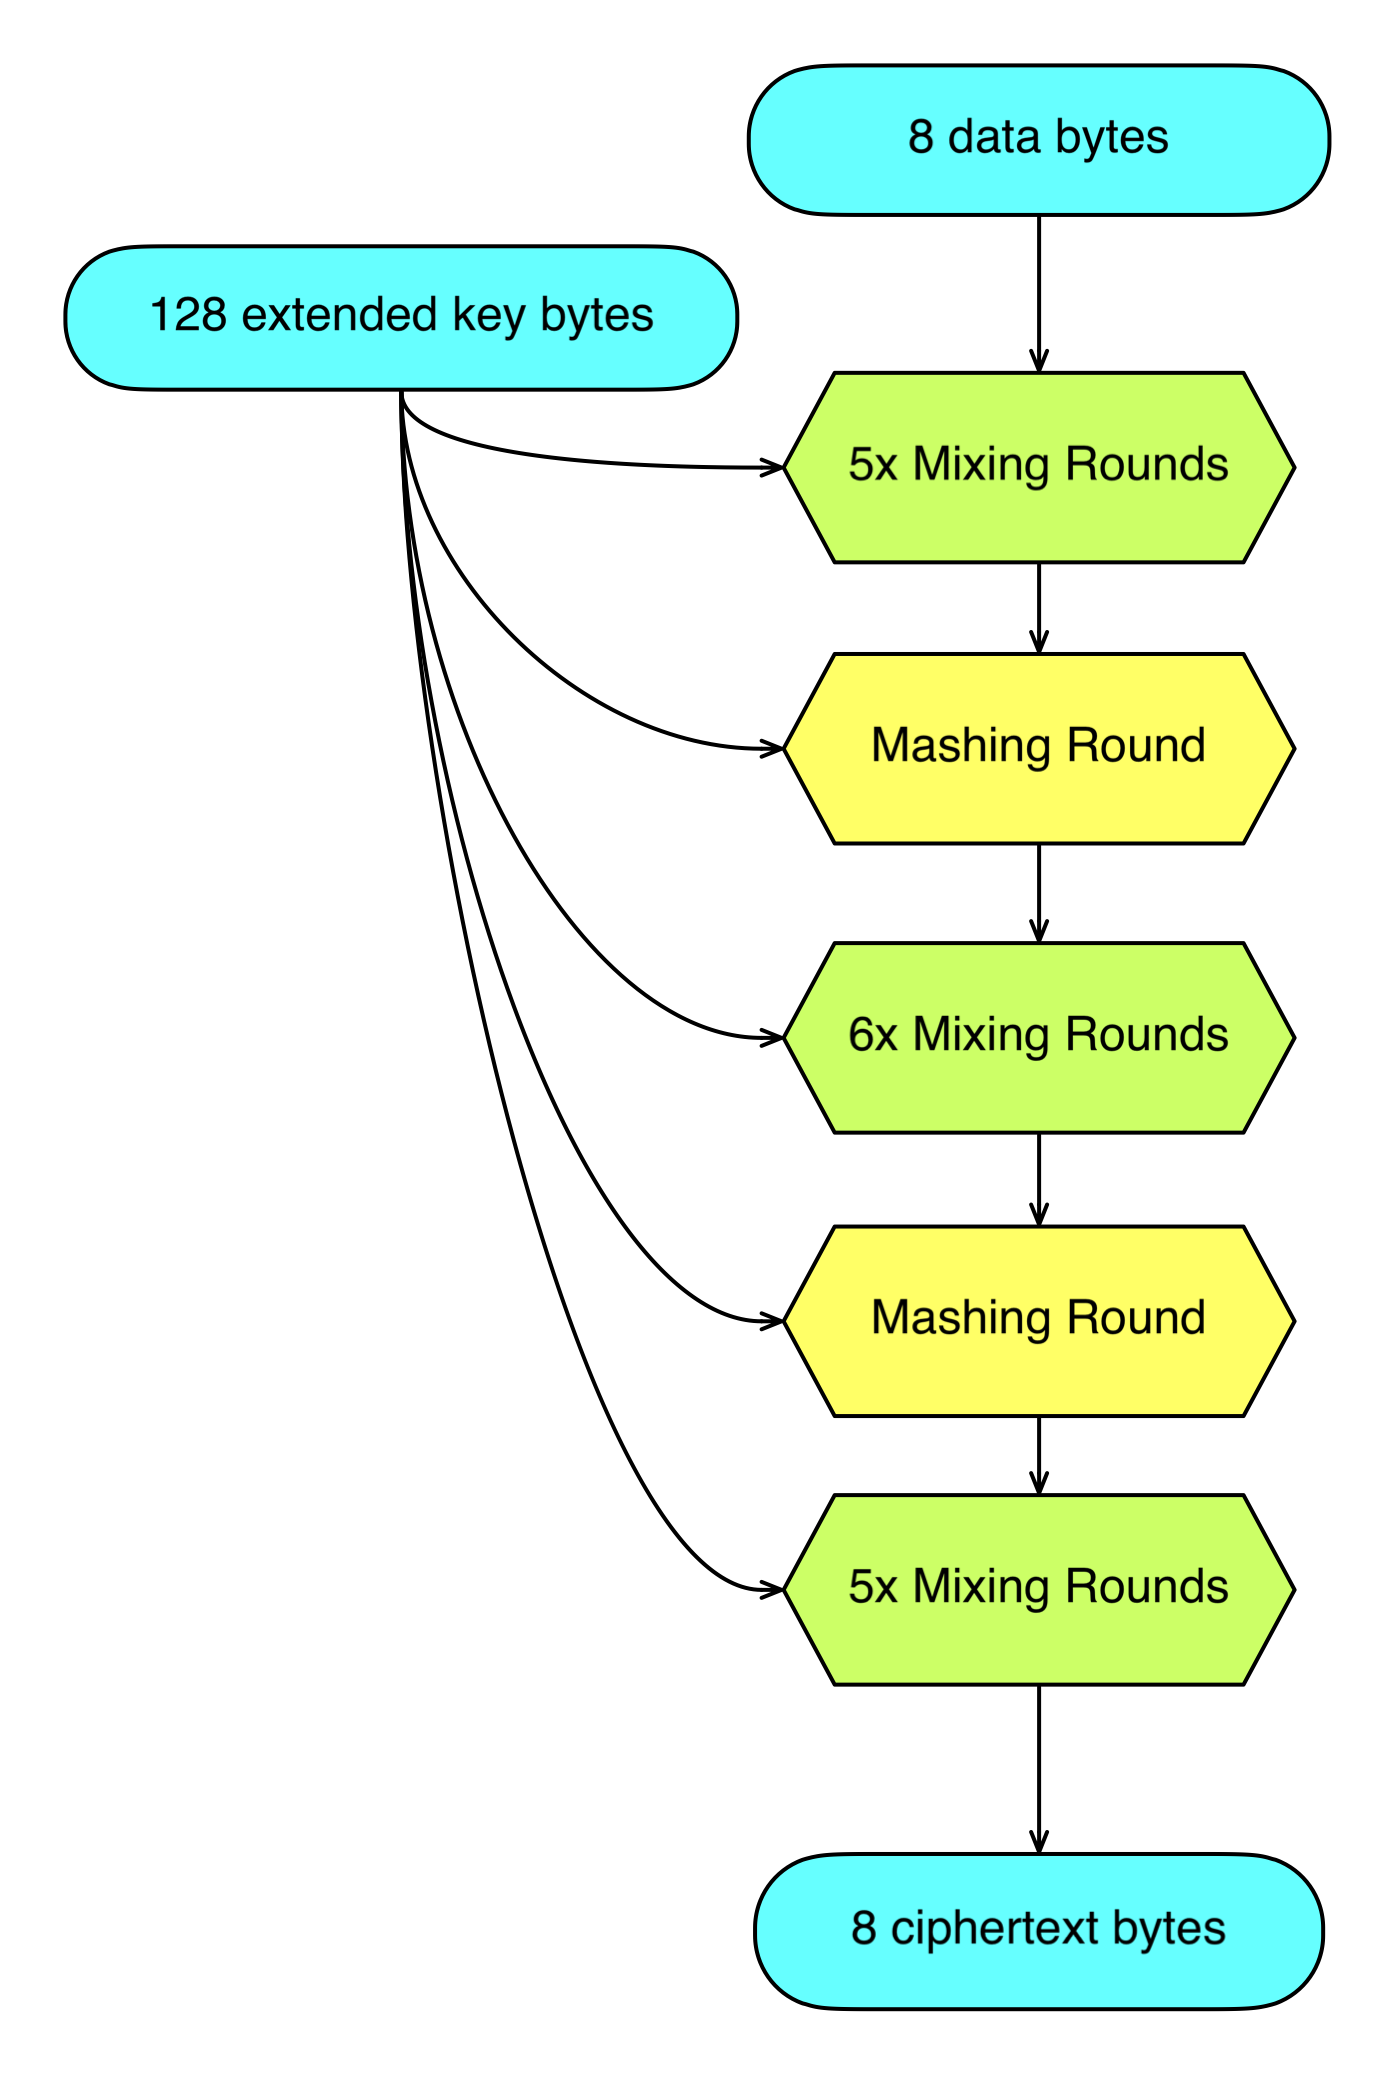
The following encryption steps are performed on every data block:
- Initialize the counter j to 0.
- Perform five Mixing Rounds.
- Perform one Mashing Round.
- Perform six Mixing Rounds.
- Perform one Mashing Round.
- Perform five Mixing Rounds.
Because every Mixing Round uses 4 key bytes, all 128 key bytes are used during encryption of one data block. The Mashing Rounds use key bytes in a more unpredicted manner.
Each Mixing Round consists of four Mixing operations, performed on four words of the data block:
- Mixing R[0]
- Mixing R[1]
- Mixing R[2]
- Mixing R[3]
Each Mashing Round consists of four Mashing operations, performed on four words of the data block:
- Mashing R[0]
- Mashing R[1]
- Mashing R[2]
- Mashing R[3]
Decryption
The decryption procedure takes as input four ciphertext words: R[0] R[1] R[2] R[3], which form one block of encrypted data. Every block of data will be decrypted by using the same 64 words of expanded secret key: K[0] K[1] ... K[63].
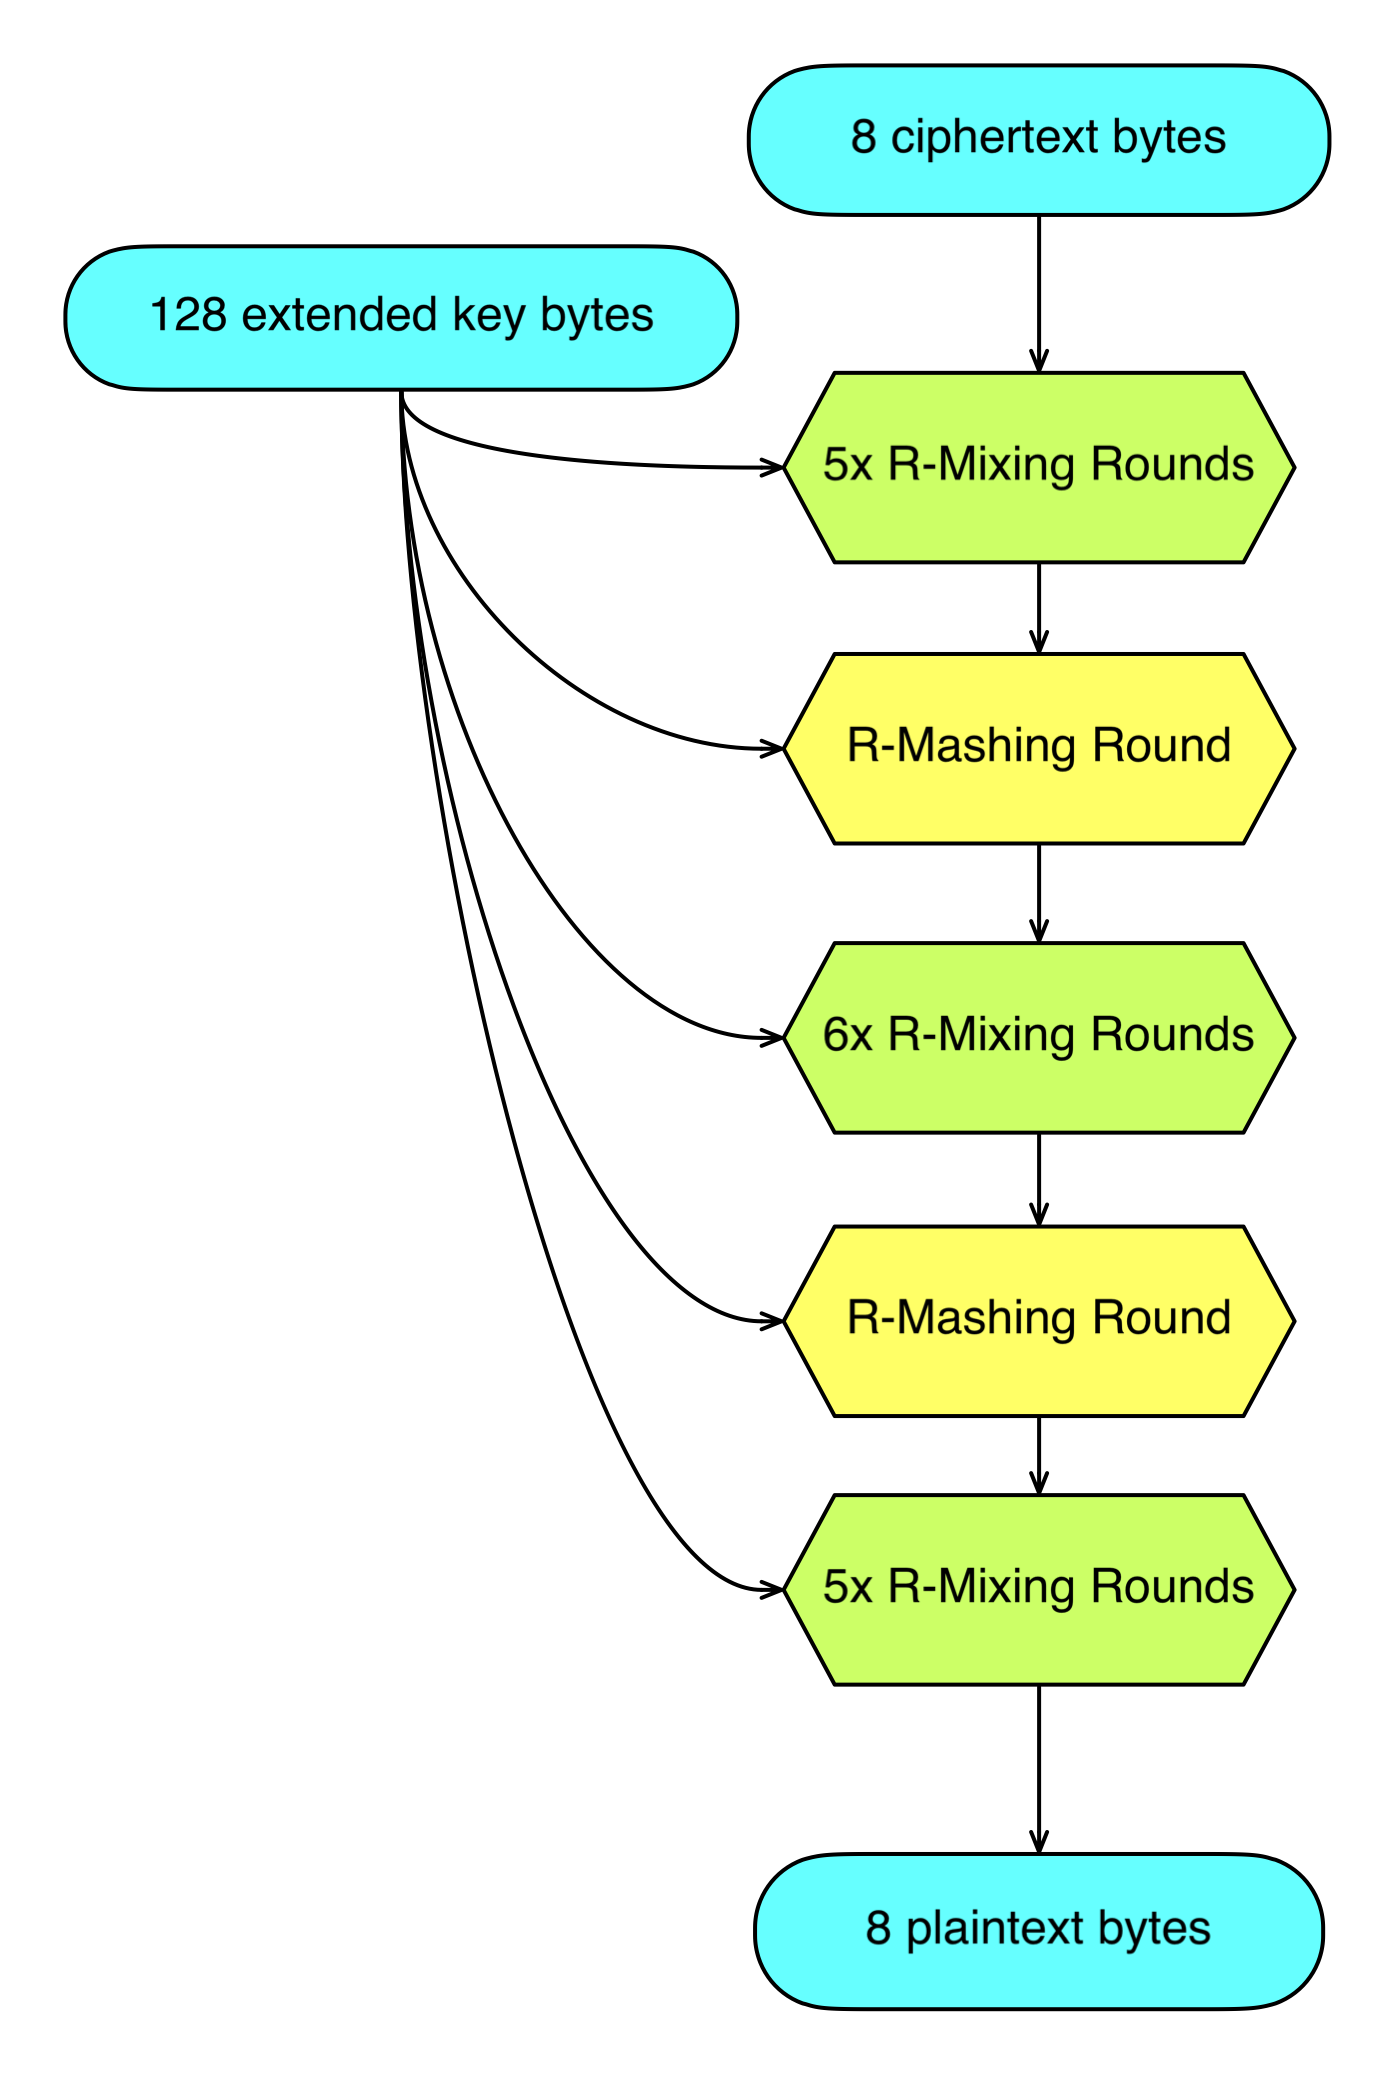
The following decryption steps are performed on every ciphertext block:
- Initialize the counter j to 63.
- Perform five R-Mixing Rounds.
- Perform one R-Mashing Round.
- Perform six R-Mixing Rounds.
- Perform one R-Mashing Round.
- Perform five R-Mixing Rounds.
Each R-Mixing Round consists of four R-Mixing operations, performed on four words of the encrypted data block:
- R-Mixing R[3]
- R-Mixing R[2]
- R-Mixing R[1]
- R-Mixing R[0]
Each R-Mashing Round consists of four R-Mashing operations, performed on four words of the encrypted data block:
- R-Mashing R[3]
- R-Mashing R[2]
- R-Mashing R[1]
- R-Mashing R[0]
Block Diagram of RC2 Encryption
Block Diagram of RC2 Decryption
Maths
The operations for RC2 algorithm are presented in the order from the low-level functions, to the more complex operations, that use the functions described above them.
Table PI (TPI)
Table PI is a fixed array that contains 256 elements, used during key expansion operations.
Table PI is filled with numbers, which are a random permutation of all possible byte values from 0 to 255. The order of numbers is based on the digits of PI: 3.1415...
| d9 | 78 | f9 | c4 | 19 | dd | b5 | ed | 28 | e9 | fd | 79 | 4a | a0 | d8 | 9d |
| c6 | 7e | 37 | 83 | 2b | 76 | 53 | 8e | 62 | 4c | 64 | 88 | 44 | 8b | fb | a2 |
| 17 | 9a | 59 | f5 | 87 | b3 | 4f | 13 | 61 | 45 | 6d | 8d | 09 | 81 | 7d | 32 |
| bd | 8f | 40 | eb | 86 | b7 | 7b | 0b | f0 | 95 | 21 | 22 | 5c | 6b | 4e | 82 |
| 54 | d6 | 65 | 93 | ce | 60 | b2 | 1c | 73 | 56 | c0 | 14 | a7 | 8c | f1 | dc |
| 12 | 75 | ca | 1f | 3b | be | e4 | d1 | 42 | 3d | d4 | 30 | a3 | 3c | b6 | 26 |
| 6f | bf | 0e | da | 46 | 69 | 07 | 57 | 27 | f2 | 1d | 9b | bc | 94 | 43 | 03 |
| f8 | 11 | c7 | f6 | 90 | ef | 3e | e7 | 06 | c3 | d5 | 2f | c8 | 66 | 1e | d7 |
| 08 | e8 | ea | de | 80 | 52 | ee | f7 | 84 | aa | 72 | ac | 35 | 4d | 6a | 2a |
| 96 | 1a | d2 | 71 | 5a | 15 | 49 | 74 | 4b | 9f | d0 | 5e | 04 | 18 | a4 | ec |
| c2 | e0 | 41 | 6e | 0f | 51 | cb | cc | 24 | 91 | af | 50 | a1 | f4 | 70 | 39 |
| 99 | 7c | 3a | 85 | 23 | b8 | b4 | 7a | fc | 02 | 36 | 5b | 25 | 55 | 97 | 31 |
| 2d | 5d | fa | 98 | e3 | 8a | 92 | ae | 05 | df | 29 | 10 | 67 | 6c | ba | c9 |
| d3 | 00 | e6 | cf | e1 | 9e | a8 | 2c | 63 | 16 | 01 | 3f | 58 | e2 | 89 | a9 |
| 0d | 38 | 34 | 1b | ab | 33 | ff | b0 | bb | 48 | 0c | 5f | b9 | b1 | cd | 2e |
| c5 | f3 | db | 47 | e5 | a5 | 9c | 77 | 0a | a6 | 20 | 68 | fe | 7f | c1 | ad |
Binary Left Rotation: <<<
The a-bit left rotation of a 2-byte word w is denoted in the algorithm as w <<< a. The leftmost a bits move to the rightmost positions.
Binary Right Rotation: >>>
The a-bit right rotation of a 2-byte word w is denoted in the algorithm as w >>> a. The rightmost a bits move to the leftmost positions.
Mixing Operation
Mixing Operation modifies one data word and increments the counter j during encryption process.
The following three operations are performed during Mixing:
R[i] = R[i] + K[j] +
+ (R[(i+4-1) mod 4] & R[(i+4-2) mod 4])
+ ((~R[(i+4-1) mod 4]) & R[(i+4-3) mod 4])
j = j + 1
R[i] = R[i] <<< s[i]
where j is the counter variable and the vector s contains the following values: s[0] = 1, s[1] = 2, s[2] = 3, s[3] = 5.
Mashing Operation
Mashing Operation modifies one data word during encryption process.
The following operation is performed during Mashing:
R[i] = R[i] + K[R[(i+4-1) mod 4] & 63]
R-Mixing Operation
R-Mixing Operation modifies one ciphertext word and decrements the counter j during decryption process.
The following three operations are performed during R-Mixing:
R[i] = R[i] >>> s[i]
R[i] = R[i] - K[j]
- (R[(i+4-1) mod 4] & R[(i+4-2) mod 4])
- ((~R[(i+4-1) mod 4]) & R[(i+4-3) mod 4])
j = j - 1
where j is the counter variable and the vector s contains the following values: s[0] = 1, s[1] = 2, s[2] = 3, s[3] = 5.
R-Mashing Operation
R-Mashing Operation modifies one data word during decryption process.
The following operation is performed during R-Mashing:
R[i] = R[i] - K[R[(i+4-1) mod 4] & 63]