- Key length = 40 bits
CSS was presented by the DVD Forum organization in 1996, as a means to encrypt DVDs content.
Usage
Because of its poor design, the effective key size is about 16 bits long.
It was compromised in 1999 by brute force attack. In this year, the application was published, which was able to quite fast break the CSS protection.
Algorithm
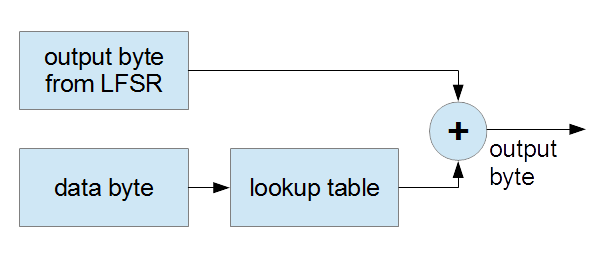
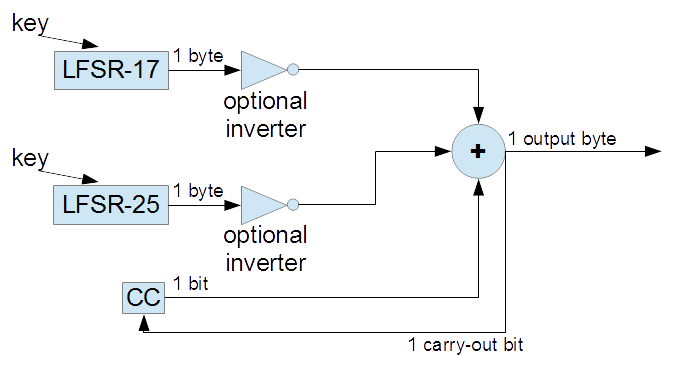
CSS is a stream cipher. The internal state machine is initialized using a 5-byte long secret key. The state machine has 42 bits and contains two . The stream of bytes is generated by registers and added XOR to stream of input data. Before addition, data bytes are changing in a lookup table and keystream bytes move through optional inverters. There are some lookup tables defined and they contain different coefficients.
The CSS cipher is created to protect audiovisual data on DVDs. There are a few different keys in the whole CSS system. They are used to mutual authentication, encryption of sectors and whole files. Some keys are stored encrypted and they must be decrypted before usage (using CSS cipher, where the encrypted data are bytes of wanted secret key).
Because of many different types of tasks of CSS - working with audiovisual data and different kind of keys - a few modes of CSS algorithm exist. All of them are generally similar but there are some differences in detail (for example coefficients in tables).
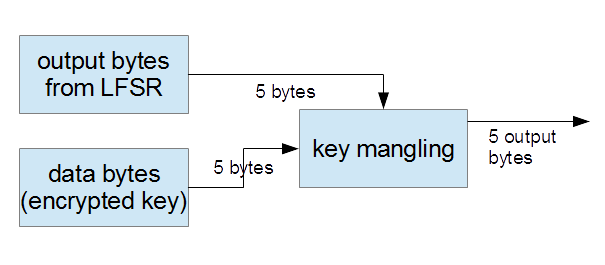
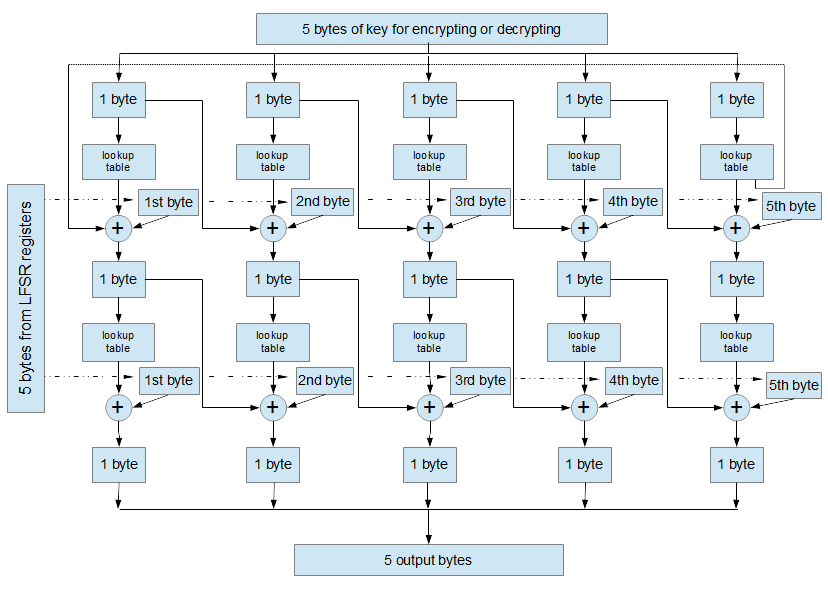
When CSS algorithm decrypts one of the secret key, 5 encoded bytes of this key are mixed with bytes received from registers in more complicated way. Instead of simple lookup tables and addition XOR with keystream, there is a key mangling operation. Each byte goes through two lookup tables and is added XOR twice with one byte from keystream.
CSS Modes
- authentication and establishing connection - the host establishes communication with DVD and both sides create a bus key,
- disc key decryption - the host receives and decrypts a disc key using one of its player keys,
- title key decryption - the host receives and decrypts a title key using the obtained disc key,
- audiovisual data decryption - using the obtained title key and a sector key read from a DVD, the host decrypts audiovisual data stored in one sector of the DVD.
CSS Keys
- player keys - stored in a DVD driver; they are used for decryption of a disc key (which is stored on DVD),
- disk key - encrypted on DVD and decrypted by the DVD driver using its player keys; it is used for decryption of a title key,
- sector key - stored unencrypted in each sector of the DVD and read by the DVD driver; it is used together with a title key for decryption of audiovisual data in one DVD sector,
- title keys - encrypted on DVD and decrypted by the DVD driver using the disc key obtained earlier; they are used for decryption of audiovisual data,
- session key or bus key - random key created during authentication between the host and DVD drive; it is used for encryption of future communication between them.
CSS System
The whole CSS system consists of three elements: a DVD, a DVD driver and a host (a computer, an application for playing DVDs).
Every DVD contains an encoded unique disc key. Similarly, each DVD driver has a few player keys. Each DVD has a hidden sector, which contains a disc key encrypted in many copies using each of the 409 existing player keys. On writeable DVDs, the hidden sector is cleared and can't be changed. A DVD driver tries to read a DVD and uses its player keys to decrypt one of the copy of the encrypted disc key on DVD.
After each try and obtaining a result, which may be a correct disc key, the DVD driver performs the following test: using received 5 bytes, which may be a disc key it tries to decrypt a test sequence (stored on DVD), which is the real disc key, encrypted using the real disc key. If the DVD driver receives the same 5 bytes like the 5 bytes it used as a key, then it is certain that those 5 bytes are the real and correct disc key.
A DVD contains usually a few encoded title keys. Each of them protect one part of the movie, called VTS (Video Title Set). Each VTS contains a set of files named as VTS_AA_B.CCC, where every A and B means one digit. CCC may be one of three possible file extensions: (.VOB, .BUP or .IFO). All the files which have the same number AA belong to the same VTS. Title keys are decrypted using the disc key.
Each data sector on DVD is 2048-byte long (so it has the same size as sectors on CD-ROMs). A sector starts with a MPEG-2 PACK header, 128-byte long. After the header there are either audiovisual data (called stream data; for example MPEG-2 data or AC-3 data) or other information (PCI or DSI). A sector key is stored unencrypted in bytes 80-84 in the header.
If a sector contains audiovisual data, then after the MPEG-2 PACK header it is stored a header of audiovisual data (stream header), which contains 2 bits determining encryption type.
- 00 - no encryption
- 01 - CSS encryption
- 10 - reserved/not used
- 11 - CPRM encryption
If a sector doesn't contain audiovisual data, those bits are not stored in this sector (because not-stream data are not encrypted).
For decryption of data stored on DVD, they are used two keys - a sector key (different value for every sector) and a title key (each DVD contains usually a few title keys, one for each VTS). First two bytes of the title key are added XOR with two first bytes of the sector key (bytes 80-81 of the sector header) and then passed into the LFSR-17 register. Last three bytes of the title key are added XOR with three last bytes of the sector key (bytes 82-84 of the sector header) and passed into the LFSR-25 register. The host obtains the title key using the disc key decrypted earlier.
On each DVD it is stored also a region code, which determine a part of world where the DVD can be played.
CSS Protocol
-
Mutual authentication
For decryption of a DVD in a DVD driver, a host must authenticate itself to the DVD using a challenge-response protocol and CSS encryption. Theoretically, the DVD must also authenticate itself to the host, however a host's application usually skips this checking. During the authentication both sides use a predefined authentication key - F4 10 45 A3 E2.
The authentication requires the following steps:
- The host receives an AGID (Authentication Grant ID) number from the DVD drive. AGID is used as a session ID for the current communication.
- The host generates 10 random bytes and sends them to the DVD driver. The driver encrypts them and sends back to the host 5-byte long sequence.
- The host decrypts driver's answer and checks if the result is the same as challenge previously sent to the driver. The DVD driver can answer using one of 32 variants, so the host must make 32 tests to check which of them has been chosen by the driver.
- The DVD driver generates a random 10-byte long sequence and sends it to the host. The host encrypts it.
- The host sends back to the driver the encrypted sequence - the new key KEY2.
- The host reads a disk key from a hidden sector on DVD.
At this point, both the host and driver know all 10 bytes - two keys created by the host and the driver. The bus key is created by encryption using the 10-byte long sequence using CSS in mode 3. It is 5-byte long and prevents to eavesdrop future communication (particularly sending title and disc keys).
If the last step is succeeded, the host will be able to read a DVD using ordinary commands SCSI read. Otherwise, the authentication fails.
-
Decoding a disk key
A DVD driver decrypts a disc key from a DVD using all its player keys. Each manufacturer of DVD drivers usually possesses one or a few player keys and uses them in his products.
-
Reading and decoding title keys
Encrypted title keys are sent from a DVD to a host. Transmitting of title keys, as well as the entire transmission in general, is encrypted using a bus key.
-
Sending encrypted data
A host reads from a DVD the whole sector of encrypted data.
-
Decoding encrypted data
A host decrypts the whole sector using an obtained title key and a sector key stored in the header of each DVD sector.
Block Diagram of CSS Algorithm for Audiovisual Data
Block Diagram of CSS Algorithm for Key Bytes
Block Diagram of CSS Additional Encryption of Keys
Block Diagram of CSS LFSR Registers
Maths
Initialisation of Registers
Based on the secret 40-bit long key, two , LFSR-17 (17-bit length) and LFSR-25 (25-bit length) and one more additional bit CC are created.
All 40 bits are divided into two LFSR registers. By assigning one letter to each bit of the key, the first order of bits may be presented as below:
KEY = jklmnopq abcdefgh QRSTUWXY IJKLMNOP ABCDEFGH
LFSR-17 = q ponmlkji hgfedcba
LFSR-25 = Y XWVUTSRQ PONMLKJI HGFEDCBA
Bits in LFSR registers are filled in the reverse order as in the key.
Bits V and i are set to 1 (to prevent ) and bit CC is set to 0.
LFSR-17 Operations
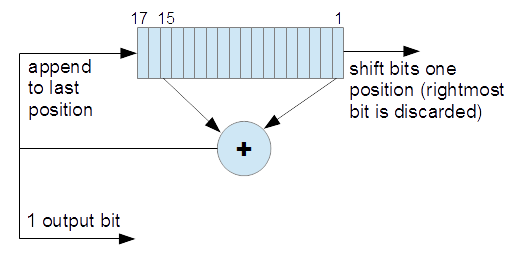
Bits are shifted right by one position. A new bit which appears in the leftmost position of the register and at the output is a sum of the first and fifteenth bits.
LFSR-25 Operations
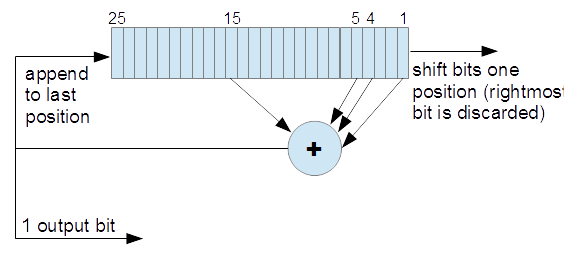
Bits are shifted right by one position. A new bit which appears in the leftmost position of the register and at the output is a sum of four bits from the register.
Inverter Modes
Depending on the current CSS mode, the inverters reverse or do not reverse output bits from LFSR registers.
The following table presents which registers and in which CSS modes reverse order of bits in each byte.
Mode |
LFSR-17 |
LFSR-25 |
|---|---|---|
| Authentication | yes | no |
| Disc key | no | no |
| Title key | no | yes |
| Audiovisual data | yes | no |
Lookup Table
Each byte for encryption or decryption is replaced by another byte, based on one of five lookup tables using in CSS. There are different tables for encryption and decryption and different tables for different CSS modes.
| 33 | 73 | 3B | 26 | 63 | 23 | 6B | 76 | 3E | 7E | 36 | 2B | 6E | 2E | 66 | 7B |
| D3 | 93 | DB | 06 | 43 | 03 | 4B | 96 | DE | 9E | D6 | 0B | 4E | 0E | 46 | 9B |
| 57 | 17 | 5F | 82 | C7 | 87 | CF | 12 | 5A | 1A | 52 | 8F | CA | 8A | C2 | 1F |
| D9 | 99 | D1 | 00 | 49 | 09 | 41 | 90 | D8 | 98 | D0 | 01 | 48 | 08 | 40 | 91 |
| 3D | 7D | 35 | 24 | 6D | 2D | 65 | 74 | 3C | 7C | 34 | 25 | 6C | 2C | 64 | 75 |
| DD | 9D | D5 | 04 | 4D | 0D | 45 | 94 | DC | 9C | D4 | 05 | 4C | 0C | 44 | 95 |
| 59 | 19 | 51 | 80 | C9 | 89 | C1 | 10 | 58 | 18 | 50 | 81 | C8 | 88 | C0 | 11 |
| D7 | 97 | DF | 02 | 47 | 07 | 4F | 92 | DA | 9A | D2 | 0F | 4A | 0A | 42 | 9F |
| 53 | 13 | 5B | 86 | C3 | 83 | CB | 16 | 5E | 1E | 56 | 8B | CE | 8E | C6 | 1B |
| B3 | F3 | BB | A6 | E3 | A3 | EB | F6 | BE | FE | B6 | AB | EE | AE | E6 | FB |
| 37 | 77 | 3F | 22 | 67 | 27 | 6F | 72 | 3A | 7A | 32 | 2F | 6A | 2A | 62 | 7F |
| B9 | F9 | B1 | A0 | E9 | A9 | E1 | F0 | B8 | F8 | B0 | A1 | E8 | A8 | E0 | F1 |
| 5D | 1D | 55 | 84 | CD | 8D | C5 | 14 | 5C | 1C | 54 | 85 | CC | 8C | C4 | 15 |
| BD | FD | B5 | A4 | ED | AD | E5 | F4 | BC | FC | B4 | A5 | EC | AC | E4 | F5 |
| 39 | 79 | 31 | 20 | 69 | 29 | 61 | 70 | 38 | 78 | 30 | 21 | 68 | 28 | 60 | 71 |
| B7 | F7 | BF | A2 | E7 | A7 | EF | F2 | BA | FA | B2 | AF | EA | AA | E2 | FF |
Linear Feedback Shift Registers - LFSR - it is a shift register, whose input bit is a linear function of its previous state.
The most popular linear function of single bits is XOR, so usually the input bit to LFSR is driven by the XOR function called for register's bits. The initial value of the LFSR is called the seed. All operations of the register are deterministic because next values produced by the register are completely determined by its current state. Because the register has a finite number of possible states, after some time it begins to produce repeating values.
LFSR registers are commonly used in counters, applications for generating pseudo-random numbers, in telecommunication and cryptography. Both software and hardware implementations are popular.
Before breaking the CSS, there aren't any DVD players working in Linux environment. It was caused by huge license fees, which must be paid to the owners of CSS rights by producers of hardware and software. After publishing a code of DeCSS in the Internet, global corporations have been trying unsuccessfully to block sharing the application.
Initialisation of the LFSR register by zeros causes that it will be producing only zeros and its state will remain zero.
The host sends SCSI command REPORT_KEY with subcode INVALIDATE_AGID to reset the drive.
Then it sends the same command REPORT_KEY with subcode GET_AGID, to obtain the AGID number.
The AGID value may be either 0x00, 0x40, 0x80 or 0xC0.
This number is added to subcodes in next SCSI commands REPORT_KEY and SEND_KEY to provide identification of the application to the drive.
The host sends SCSI command SEND_KEY with subcode SEND_CHALLENGE_KEY and AGID number. It attachs a random (10-byte long) challenge sequence.
Then it sends SCSI command REPORT_KEY with subcode GET_KEY1 and AGID number.
The host receives from the driver 5-byte long response - a key KEY1.
The host determines the variant which is used by the driver, by encrypting its challenge (10-byte long). It uses CSS algorithm in mode 3 for key KEY1.
The host encrypts the challenge 32 times, once for each variant (from 0 to 31). Then it takes the variant for which KEY1 received from the driver and KEY1 calculated by itself are the same.
The host sends SCSI command REPORT_KEY with subcode GET_CHALLENGE and AGID number.
The driver returns a 10-byte long challenge.
Then the host encrypts the challenge using CSS algorithm in mode 3 for key KEY2 and the variant calculated in the previous step. The result is a 5-byte long KEY2.
The host sends KEY2 to the DVD driver using SCSI command SEND_KEY with the subcode SEND_KEY2 and AGID number.
The bus key is calculated using the CSS algorithm in mode 3 for bus key (BUSKEY) and using the variant specified before. Keys KEY1 and KEY2 are concatenated and sent to encryption. A 5-byte long bus key is received as a result.
The host sends to the driver an SCSI command READ_DVD_STRUCTURE with subcodes GET_DISK_KEY and AGID number.
The received disc key is adding XOR with the bus key.